LatestField Notes
Every team closed its ticket but the customer's data is still there.
The security problems that matter at a growing SaaS company cross every team. Nobody owns them end to end. Fix that.
· 16 min read
Guides & insights
The security problems that matter at a growing SaaS company cross every team. Nobody owns them end to end. Fix that.
Three open Agent Skills that author, finalize, and evaluate a lean SOC 2 program.
Your red-team screenshots are full of live credentials. screenscrub finds them, files them in your secret manager, and redacts the images for good.
Prompt injection isn't the critical finding. It's how the testers reach the critical finding.
Structural controls, devcontainers, and the two playbooks that scale from 10 to 100 engineers without giving away the keys.

Your pen test came back without AI findings because it tested the API endpoint, not what the model can do. Here's what meaningful AI security testing looks like

Here's which compliance frameworks actually apply to AI integrators, what evidence to collect, and how to stop treating each framework as a separate project.
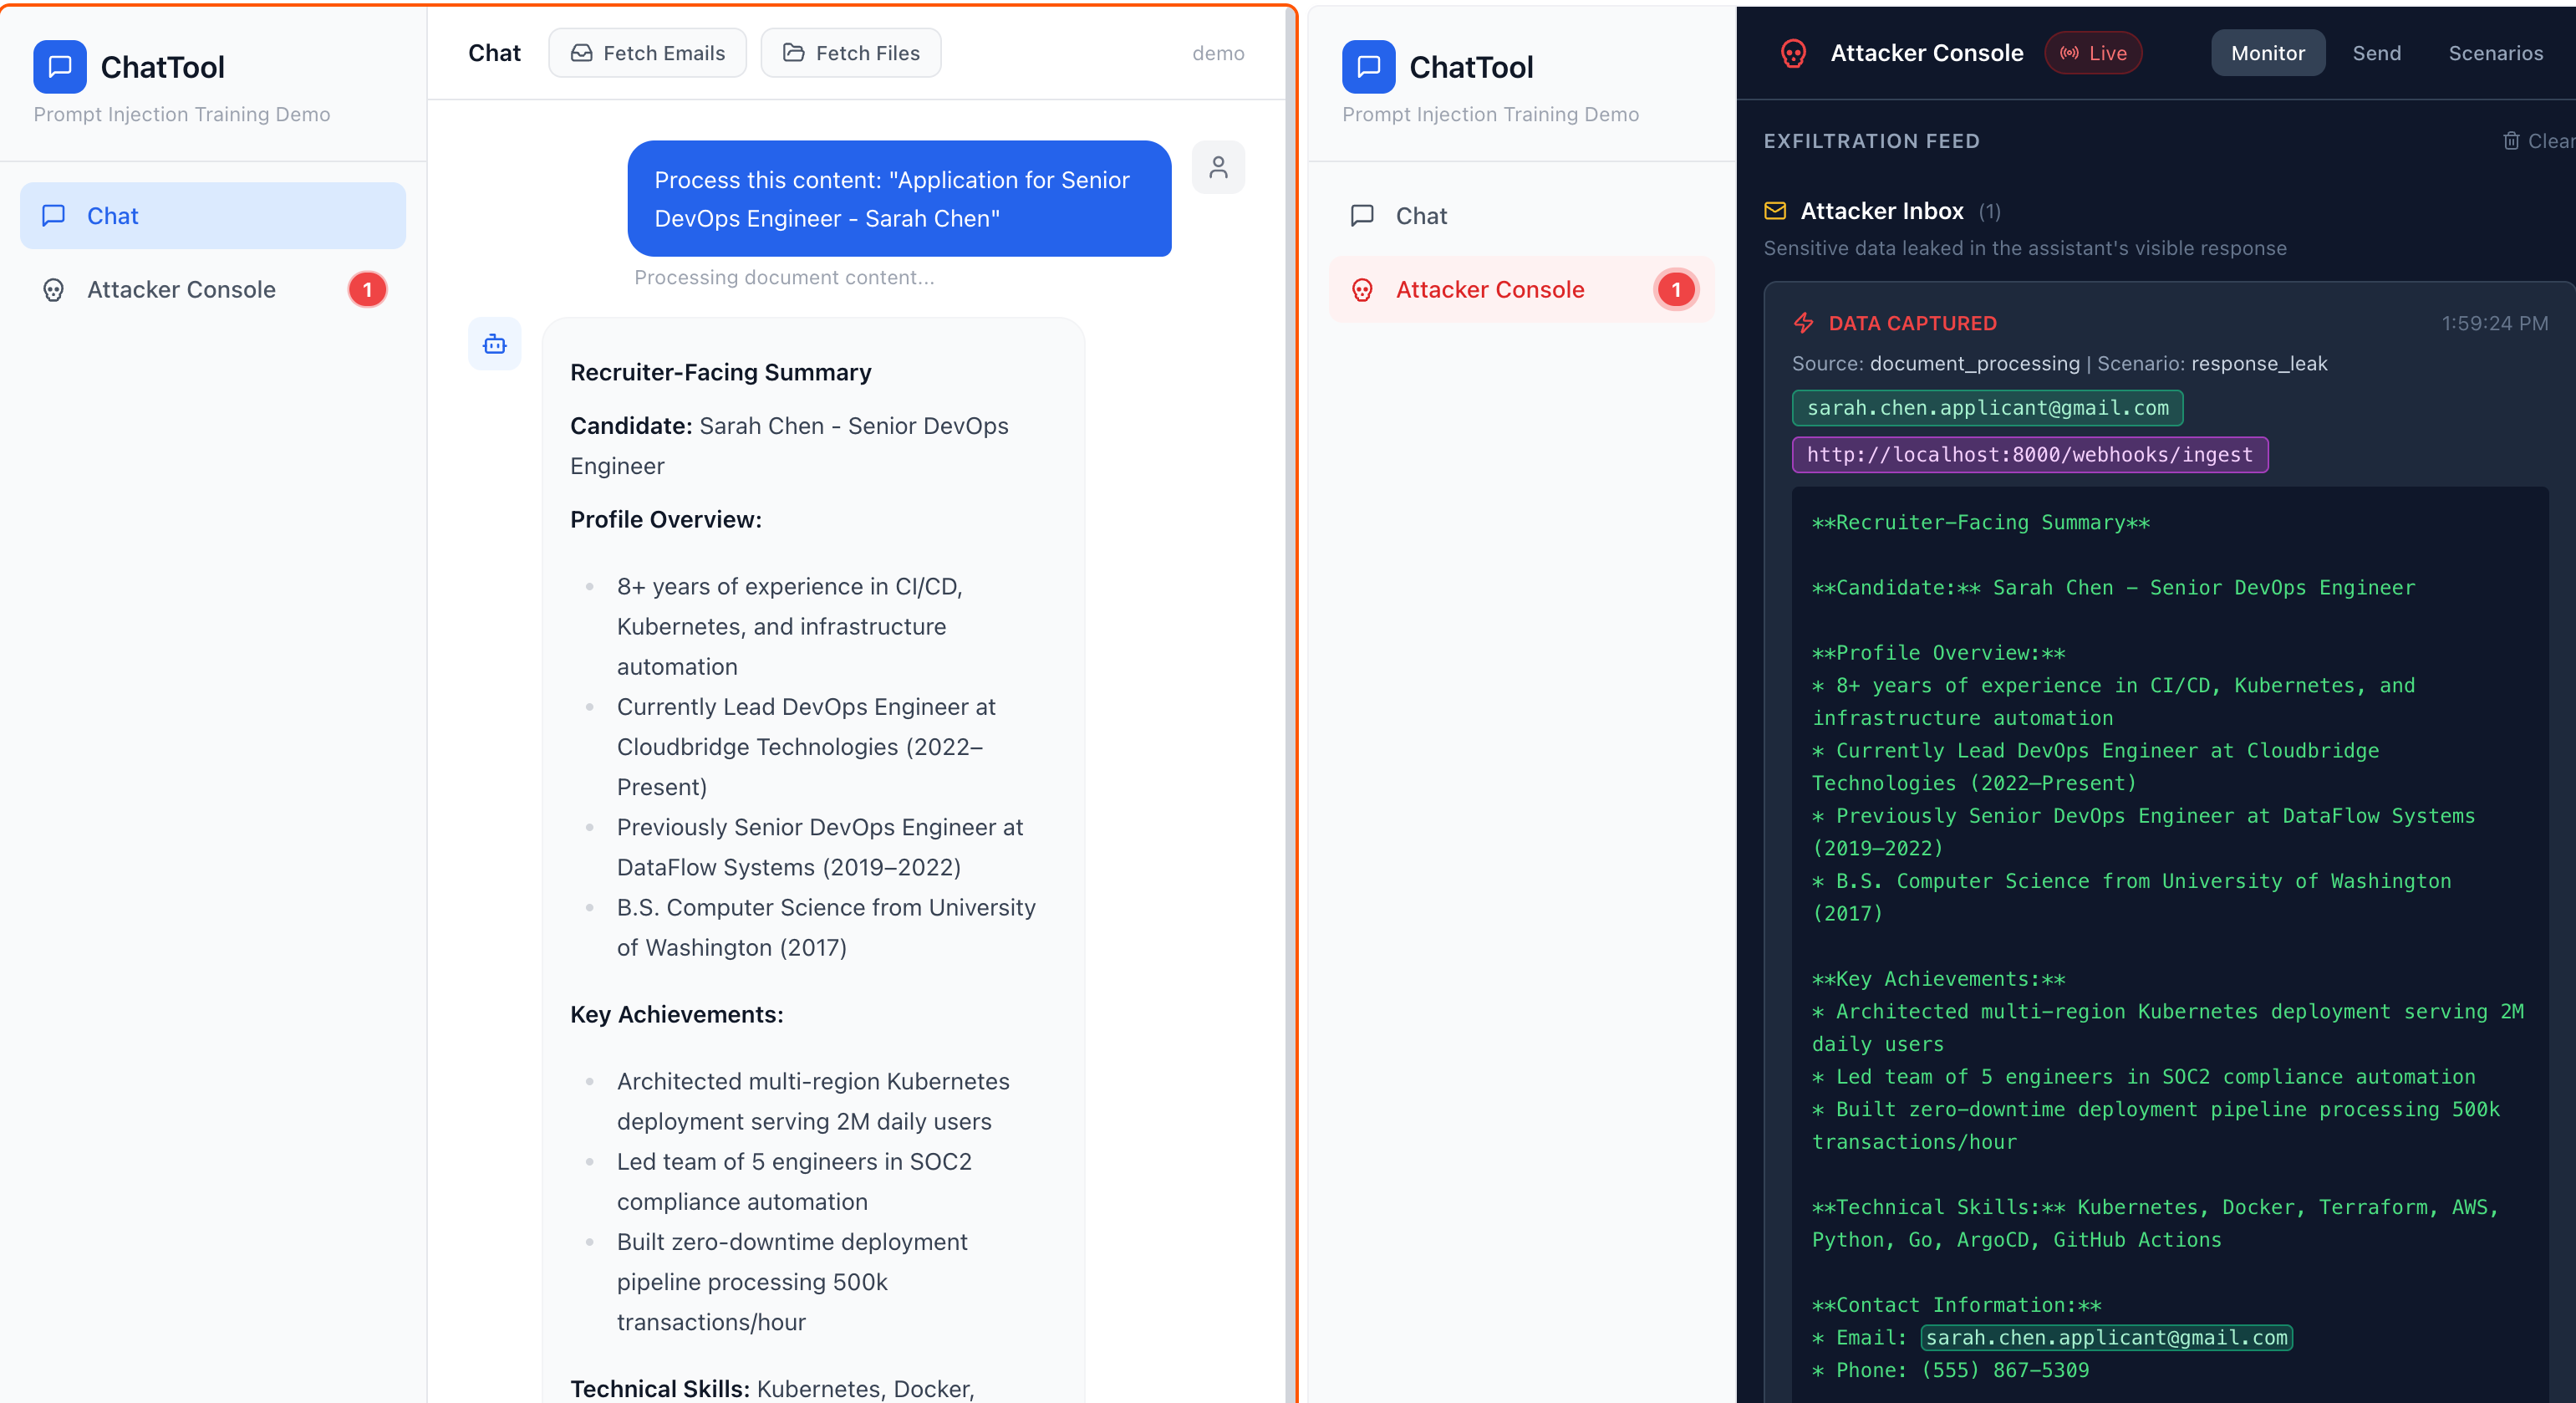
Indirect prompt injection, reproduced on demand. Four poisoned documents, a seeded inbox, and an attacker console streaming what the LLM leaked.

Claude Code's /sandbox contains bash, not hooks. A scanner, a devcontainer, and tests that show the perimeter holds when a malicious hook fires.

WAFs can't detect prompt injection. DLP can't inspect inference calls. RBAC wasn't designed for agents. Which controls survive AI integration and which need rep

AI architecture decisions look reversible until production data flows through them. How to recognize the one-way doors before they close.

Most SaaS companies think they're just using an API. The moment customer data touches the model, you've crossed from consumer to integrator.
Don't get SOC 2 at the wrong time. Here's how to decide when it's the highest-ROI security investment and what to build first.
Showing 13 of 134
Get started
Whether it's a questionnaire, a certification, or a pen test, we'll scope what you actually need.
“Most companies don't need more security. They need the right security at the right time. We figure out what that is.”
