Skip to content

NIST CSF & CMMC

Government and defense contracts come with compliance requirements that can look overwhelming at first glance: NIST Cybersecurity Framework, CMMC, and others.

We help you understand what's actually required for your situation, build a realistic plan to get there, and avoid over-engineering things that don't need to be complicated.

Modern red office building with blue-tinted glass windows against a bright sky
NIST CSF and CMMC

01NIST CSF and CMMC

How NIST CSF & CMMC works with Adversis

We assess where you stand against federal security frameworks, map out what needs to change, and help you build the documentation and controls required for certification without over-engineering.

What's included

  1. 1. Gap assessment and remediation planning
  2. 2. Policy development and control implementation
  3. 3. Auditor coordination and prep
  4. 4. Certification progression support

02Is this you?

Who it's for

SaaS companies entering government, defense, or regulated enterprise markets where NIST CSF or CMMC is required.

The outcome

A clear path to certification and the documentation to prove you've walked it.

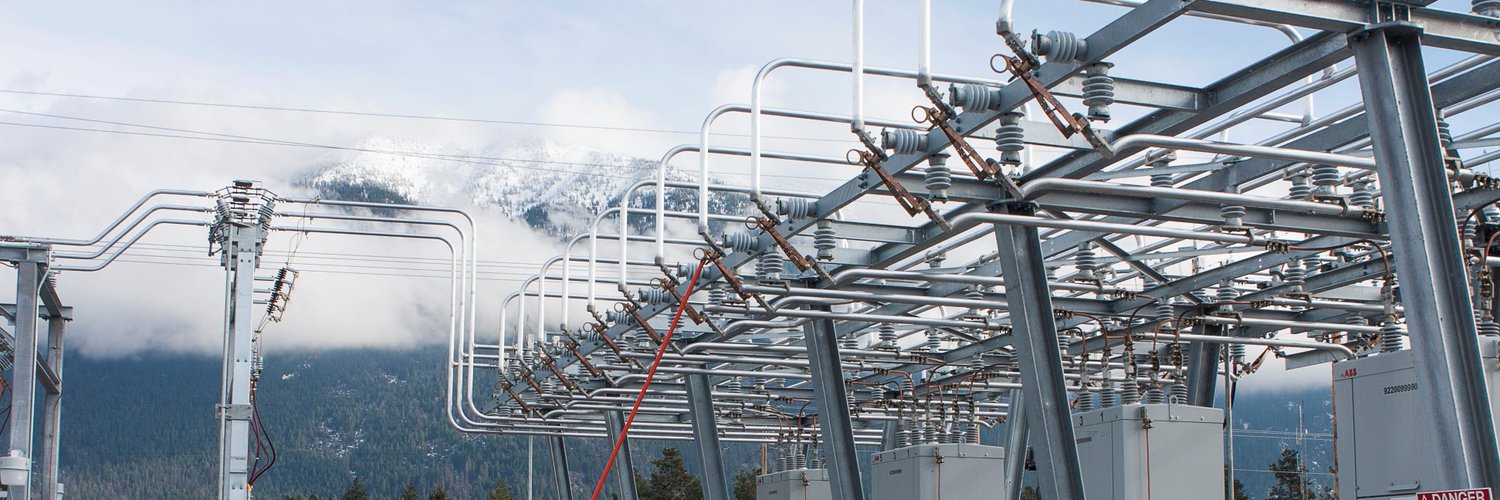
Regional Electrical Utility project
Electrical UtilityNetwork Penetration TestingSecurity Advisory

Case study

A regional utility partnered with Adversis to validate network segmentation, assess infrastructure security, and satisfy NERC compliance requirements, emerging with a clear prioritization framework and resources secured for ongoing improvements.

Challenge
The utility's cybersecurity team had completed significant security upgrades and needed independent validation that their controls held up under real-world testing. With NERC guidance requiring regular penetration testing and member data protection at stake, they needed more than a checkbox assessment.
Solution
Adversis worked alongside the internal team to prioritize network segments for assessment and tailor coverage to their specific validation needs. Using advanced techniques drawn from Fortune 500 offensive security experience, the engagement went beyond standard kill-chain methodology to evaluate realistic attack scenarios against the utility's infrastructure.
Result
100%NERC compliance requirements satisfied, with validated controls and a strategic roadmap that helped the team secure additional resources for training and continued security investment.
FAQ

Straight answers to what teams usually ask us before we start. If yours isn't here, ask us directly.

  • Mostly B2B SaaS companies, typically Series A or B, with a small security team or none at all. The common thread: enterprise buyers are asking hard security questions, and the team needs help answering them.

  • Keep using them. They're great at automating evidence collection and getting you through your SOC 2 audit. We pick up where they stop: the live security call with your prospect's team, the custom questionnaire questions that fall outside your audit scope, and pen testing that holds up when a buyer's security team actually reads the report. Instead of your CTO spending weeks figuring out what enterprise buyers expect and how to talk about your security posture, you hand it to us. Compliance platforms get you the certificate. We get you through the security review.

  • Yes. But we'll probably ask what's driving the need, because a pen test is often part of a bigger picture (a deal in motion, a compliance requirement, a buyer's security review). If you genuinely just need a clean report, we can do that, validation and retesting included. If there's more to untangle, we'll tell you.

  • Yes, and we can get on calls with your buyer's security team when needed. We've been on the other side of those calls, running vendor evaluations. We know what they're actually trying to learn and how to answer in a way that builds confidence. We've also been on both sides of a breach and can justify when controls make a difference.

  • Most engagements kick off within 2-3 weeks. If you have a deal on the line and need to move faster, tell us. We'll see what we can do.

  • Both. Some clients need a pen test or SOC 2 sprint and we're done. Others want a retained advisor they can pull in for security reviews, architecture questions, or board prep. We structure it around what you actually need.

  • It depends on scope, but most companies spend less on a full engagement than they lose in delays. A pen test or gap analysis starts in the low five figures. A broader security story or compliance push scales from there based on what you actually need.

  • That's most of our clients. We act as your security bench: fractional expertise you can tap without hiring a full team. When you're ready to build internally, we can help with that transition too.

Get started

Whether it's a questionnaire, a certification, or a pen test, we'll scope what you actually need.

Chad Nelson
Chad NelsonCo-Founder, Head of Business Development
“Most companies don't need more security. They need the right security at the right time. We figure out what that is.”
Made with Modulify